orchestrata_ultimate.kernel.audit
Reference › orchestrata_ultimate › kernel › audit
Audit trail logging subsystem (decomposed from audit_logger).
The audit trail of the kernel package. Routing decisions, policy queries, escalations, session and volk lifecycle events and similar records are written here so that a run can be reconstructed afterwards. The package was split out of a single audit_logger module, and the old module survives as the shim audit_logger. The package serves SPEC-001 story US-008.
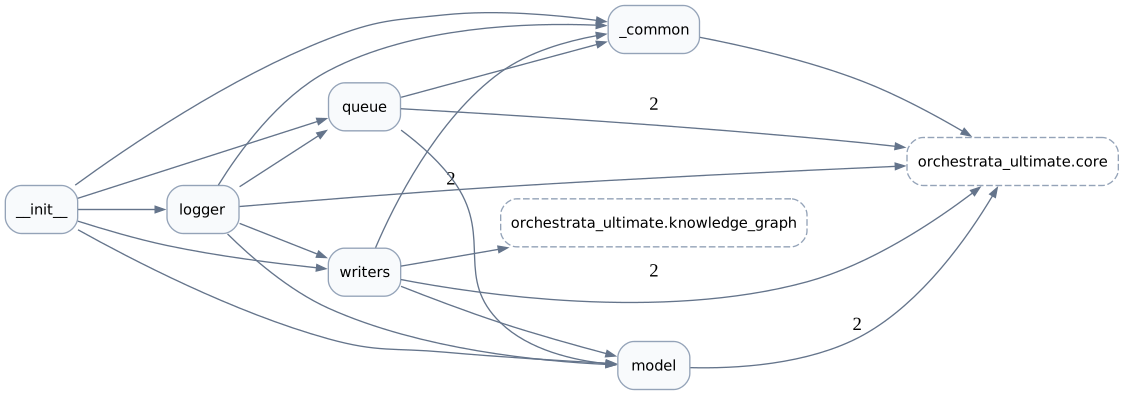
The parts, by role:
- Model: model defines
AuditEventType,AuditOutcome,AuditEntryandAuditLogConfig. - Service: logger holds
AuditLogger, which buffers entries, runs the flush and worker loops, and offers typedlog_*helpers plus query and export methods. - Durable hand-off: queue holds
RedisAuditQueue, so callers can enqueue and move on. - Storage: writers holds the base
AuditLogWriter, the file writer with rotation and the graph writer. - Support: _common and the re-exporting init.
Data flows in one direction. A caller creates an entry through a log_* helper; AuditLogger.log enqueues it in Redis when the queue is available, otherwise it buffers it. A worker (or the buffer flush) hands it to every writer, which appends it to a JSON-lines file and creates a graph node. Failures in any step are logged, not raised, so audit never stops the pipeline.
The entry points are outside the package: audit_bootstrap builds the default logger and offers fire_and_forget_audit, and the pipeline_audit mixin wires it into PipelineRunner. Start reading at logger.
6 modules, 1,642 lines of code.
Modules
| Module | Summary | LOC |
|---|---|---|
__init__ |
Audit trail logging subsystem (decomposed from audit_logger). | 38 |
_common |
Shared audit primitives: logger, optional-backend flags, time helper. | 30 |
logger |
Main audit logging service with buffered writes and query capabilities. | 832 |
model |
Audit event types, outcomes, entry, and configuration models. | 214 |
queue |
Redis-backed audit queue for durable fire-and-forget logging. | 147 |
writers |
Audit log writers: base, file-based, and graph-based destinations. | 381 |
Dependency diagram